
Physical Push Keys (packages/hardware-keys)
Connect physical FIDO2 and U2F authenticators—such as the YubiKey 5 Series, Security Key C NFC, SoloKey, and Nitrokey—directly to your Linux desktop, SSH keys, Git commits, sudo prompts, and the RobOS Pass Store.
Table of contents
1. Architecture Overview
RobOS Hardware Keys (packages/hardware-keys, debug port :19218) combines three local Linux inspection layers—/sys/class/hidraw udev attributes, YubiKey Manager (ykman), and direct python3-fido2 CTAP2/CTAP1 HID frames—so every hardware capability can be inspected and exercised without cloud services or browser extensions.
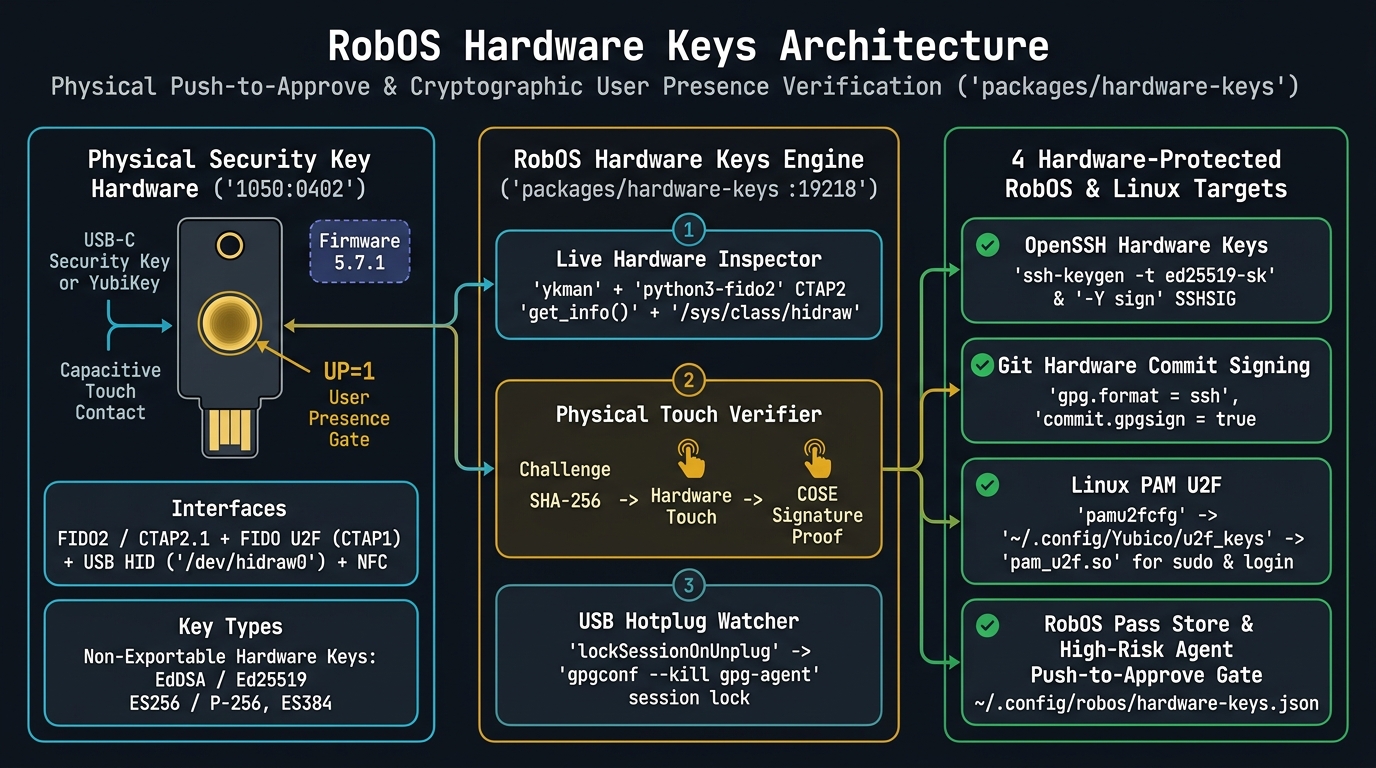
flowchart LR
  subgraph HW["Physical Security Key (USB 1050:0402 / NFC)"]
    TOUCH["Gold Capacitive Touch Disc<br/>Hardware User Presence (UP=1)"]
    SE["Secure Element (Firmware 5.7.1)<br/>FIDO2 CTAP2.1 + FIDO U2F CTAP1<br/>COSE: EdDSA (-8), ES256 (-7), ES384 (-35)"]
    HID["Linux Kernel HID Node<br/>/dev/hidraw0 (udev ACL crw-rw----+)"]
    TOUCH --> SE --> HID
  end

  subgraph ENGINE["RobOS Hardware Keys Studio (packages/hardware-keys :19218)"]
    INSP["Hardware Inspector<br/>sysfs + ykman + python3-fido2 Ctap2.get_info()"]
    CHAL["Physical Touch Verifier<br/>SHA-256 Challenge -> Touch -> Signature Proof"]
    HOTPLUG["USB Hotplug Monitor (3.5s poll)<br/>Auto-Lock on Unplug (gpgconf --kill gpg-agent)"]
    HID --> INSP
    HID --> CHAL
    HID --> HOTPLUG
  end

  subgraph TARGETS["Protected Workstation & RobOS Targets"]
    SSH["OpenSSH 10.2 FIDO2 Keys<br/>~/.ssh/id_ed25519_sk & ssh-keygen -Y sign"]
    GIT["Git Commit Signing<br/>gpg.format = ssh & commit.gpgsign = true"]
    PAM["Linux PAM U2F<br/>pamu2fcfg -> ~/.config/Yubico/u2f_keys"]
    GUARD["RobOS Pass Store & Agent Gate<br/>~/.config/robos/hardware-keys.json"]
  end

  ENGINE --> SSH
  SSH --> GIT
  ENGINE --> PAM
  ENGINE --> GUARD
2. Live Application Views
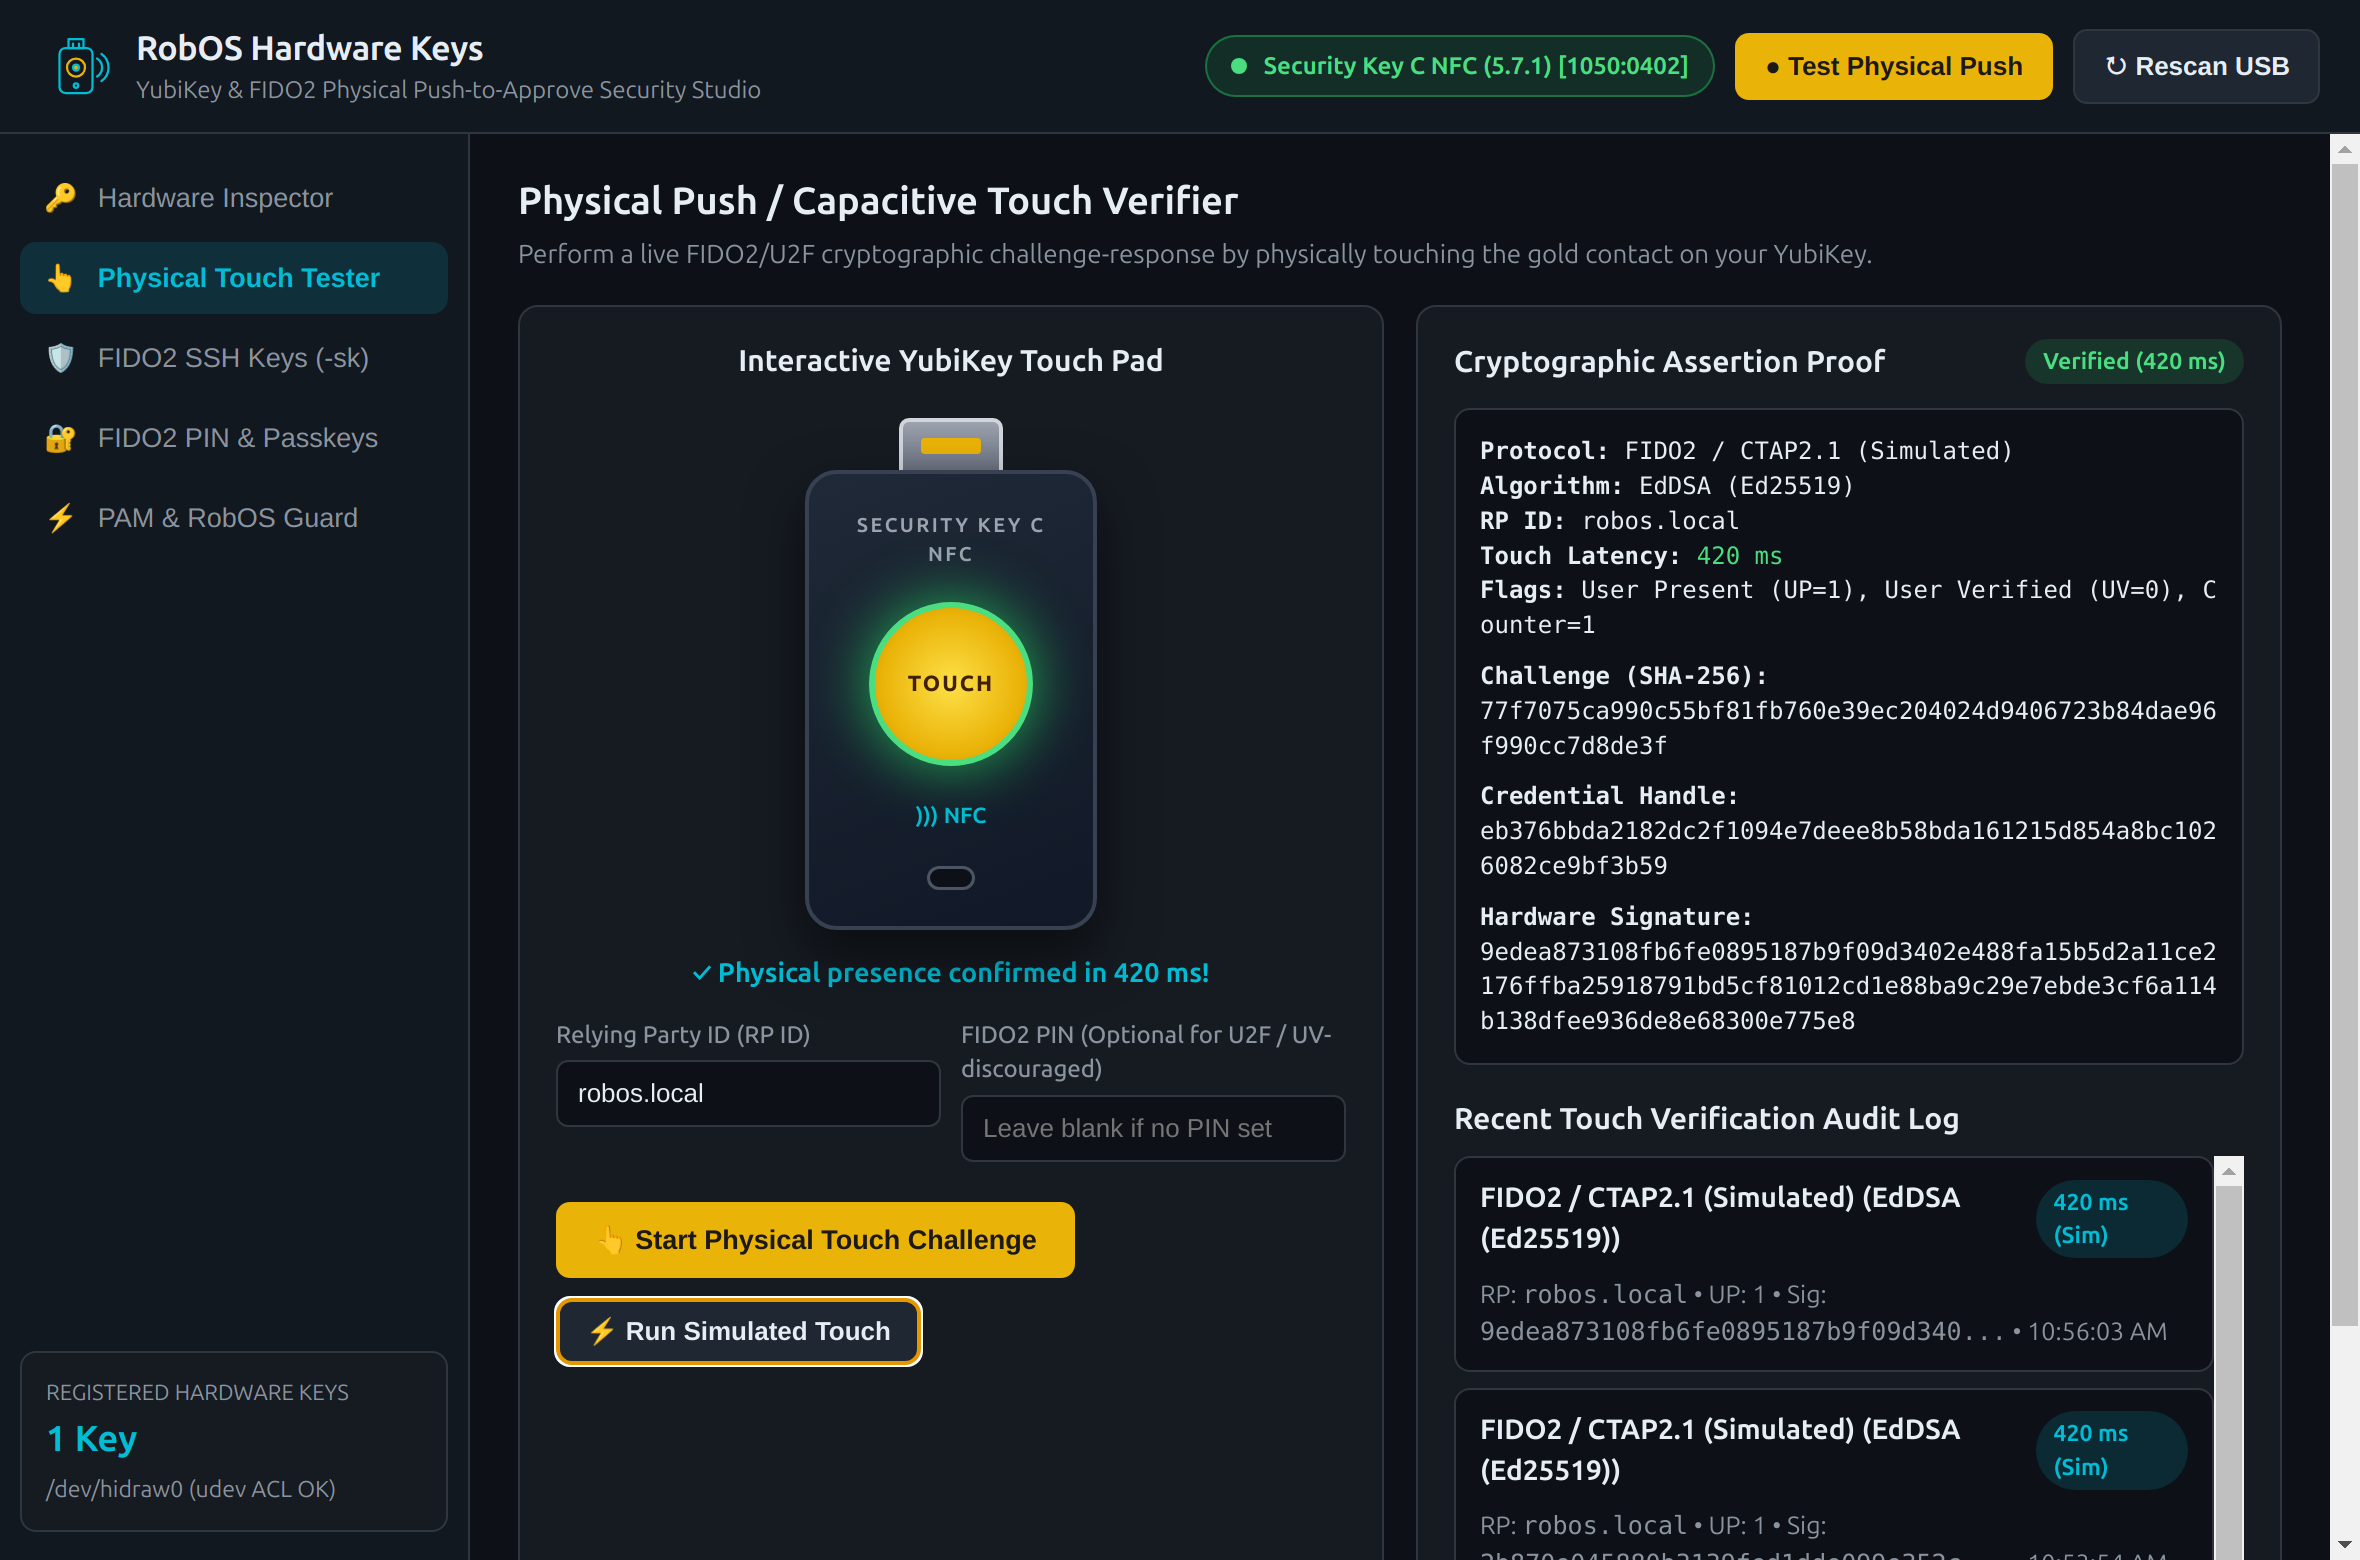
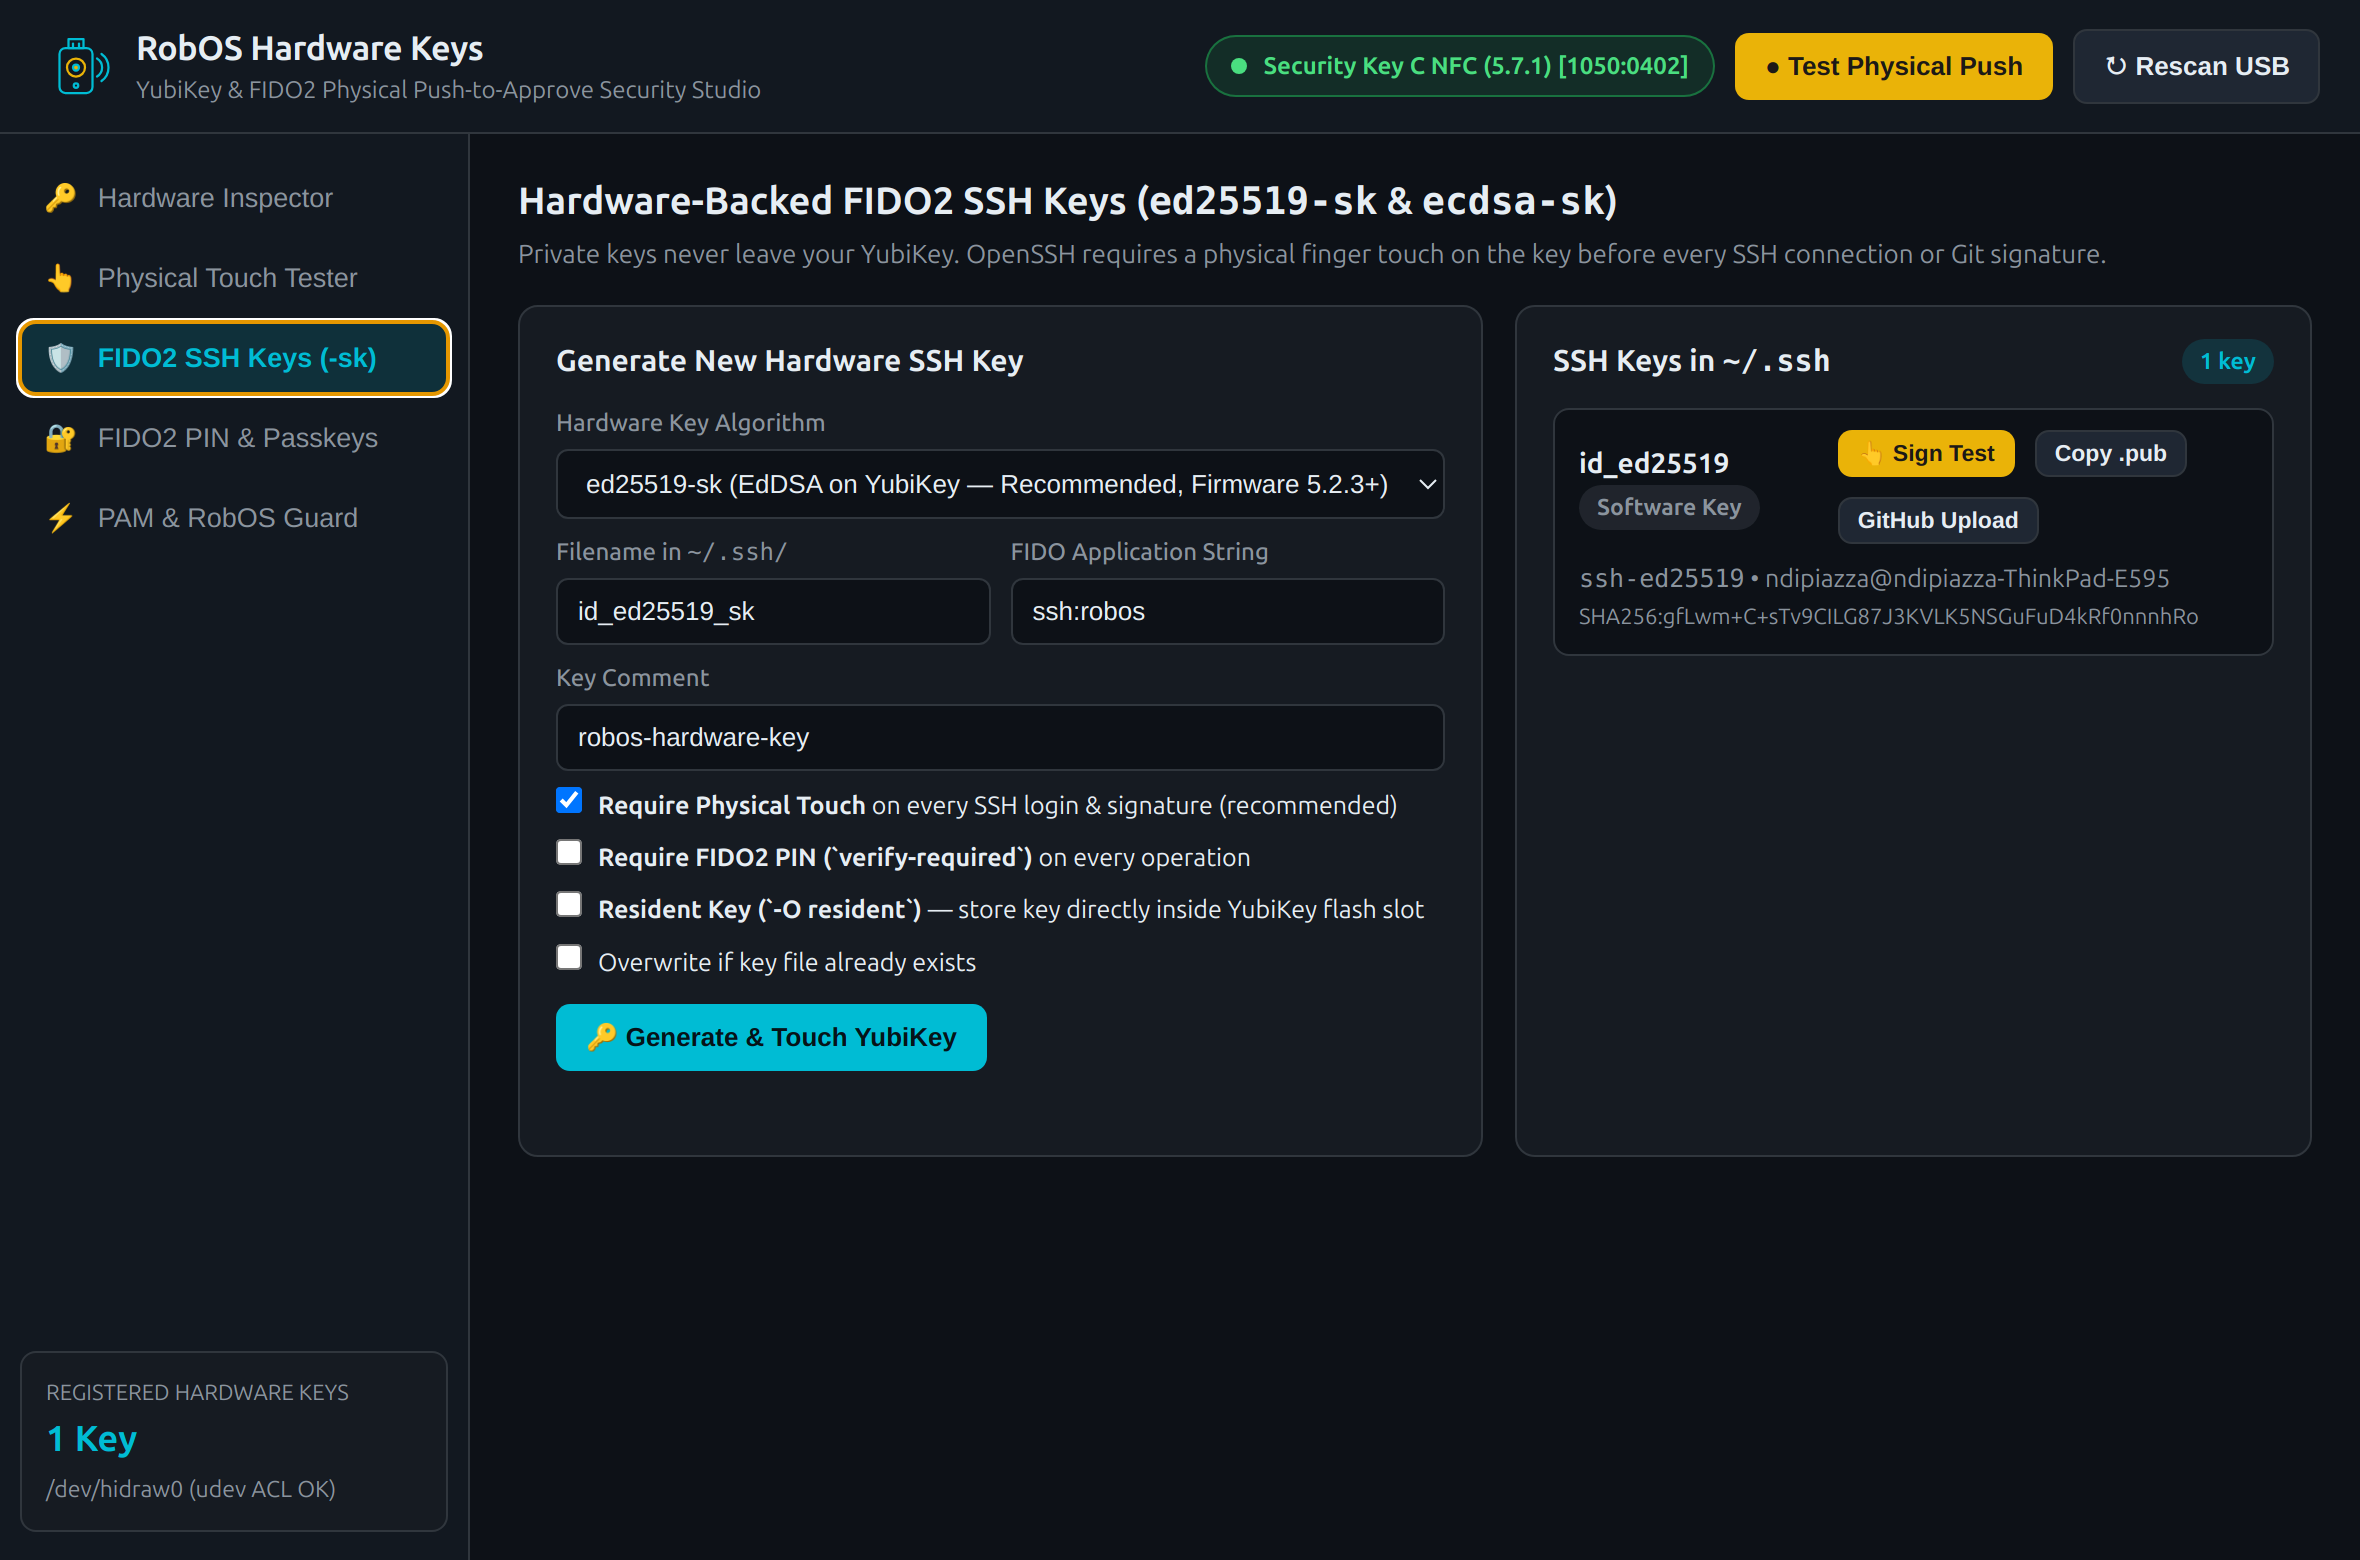
| Physical Touch Verifier | FIDO2 SSH Keys (ed25519-sk) |
|---|---|
 |  |
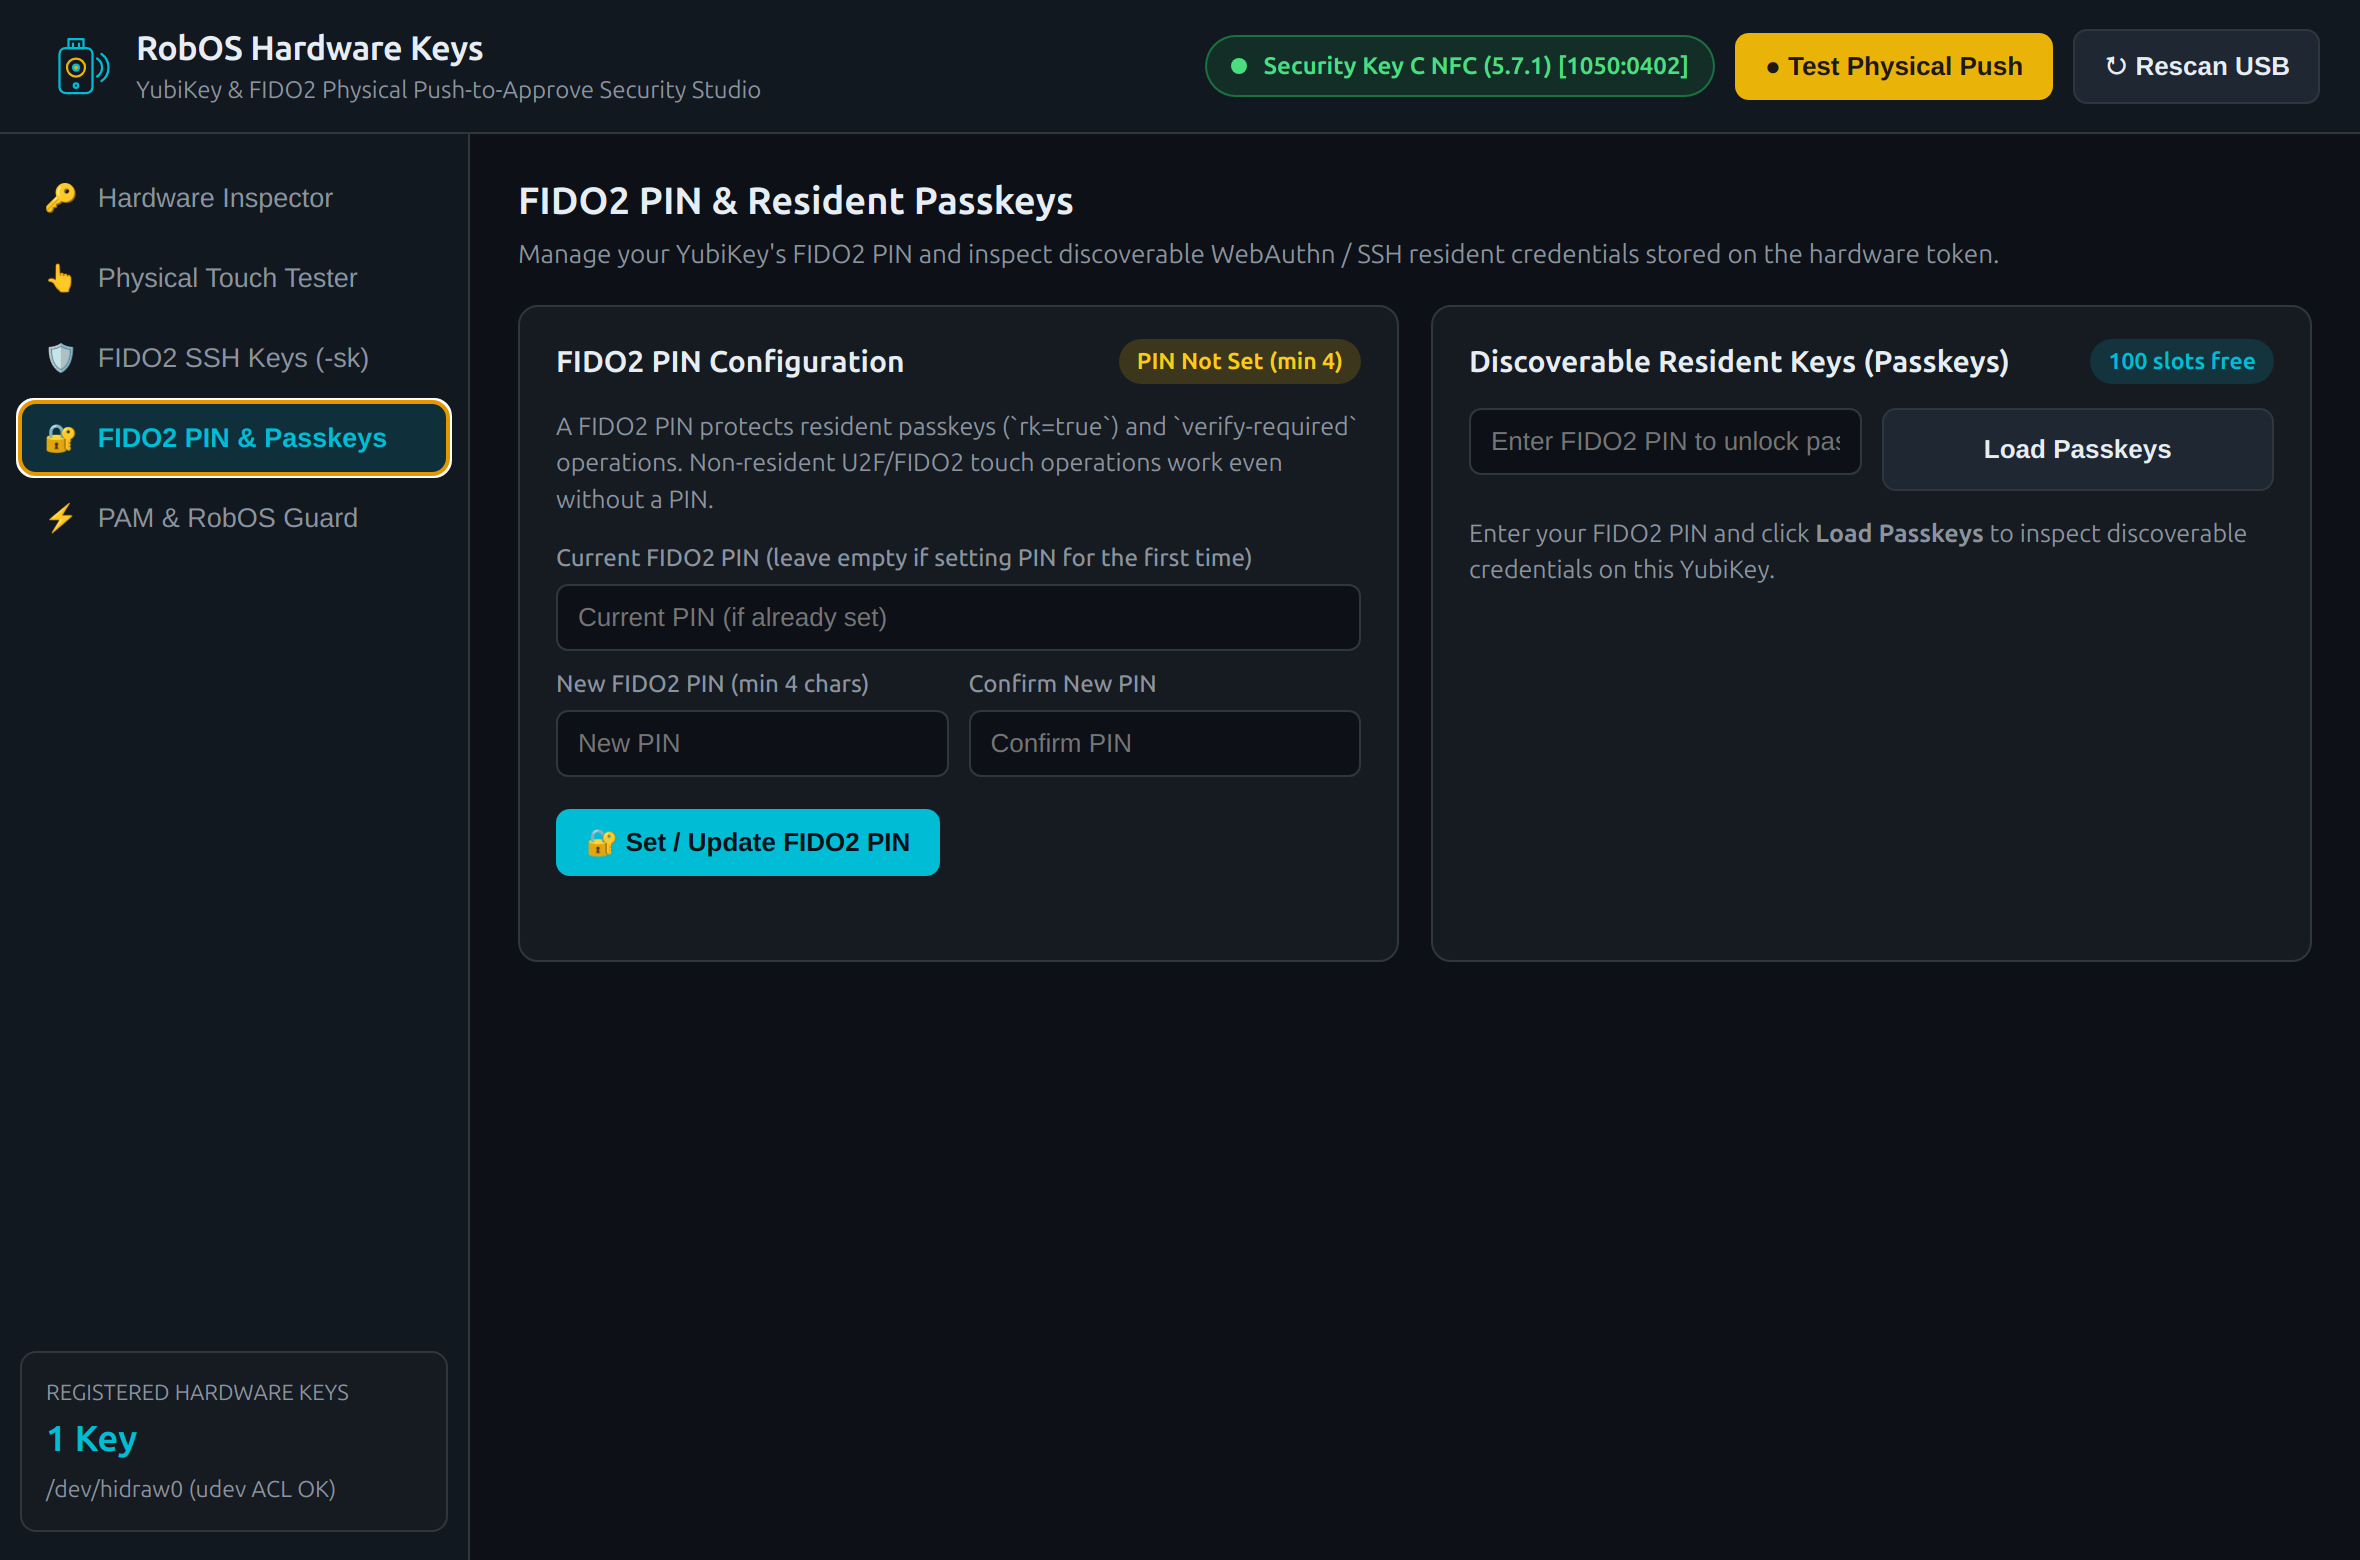
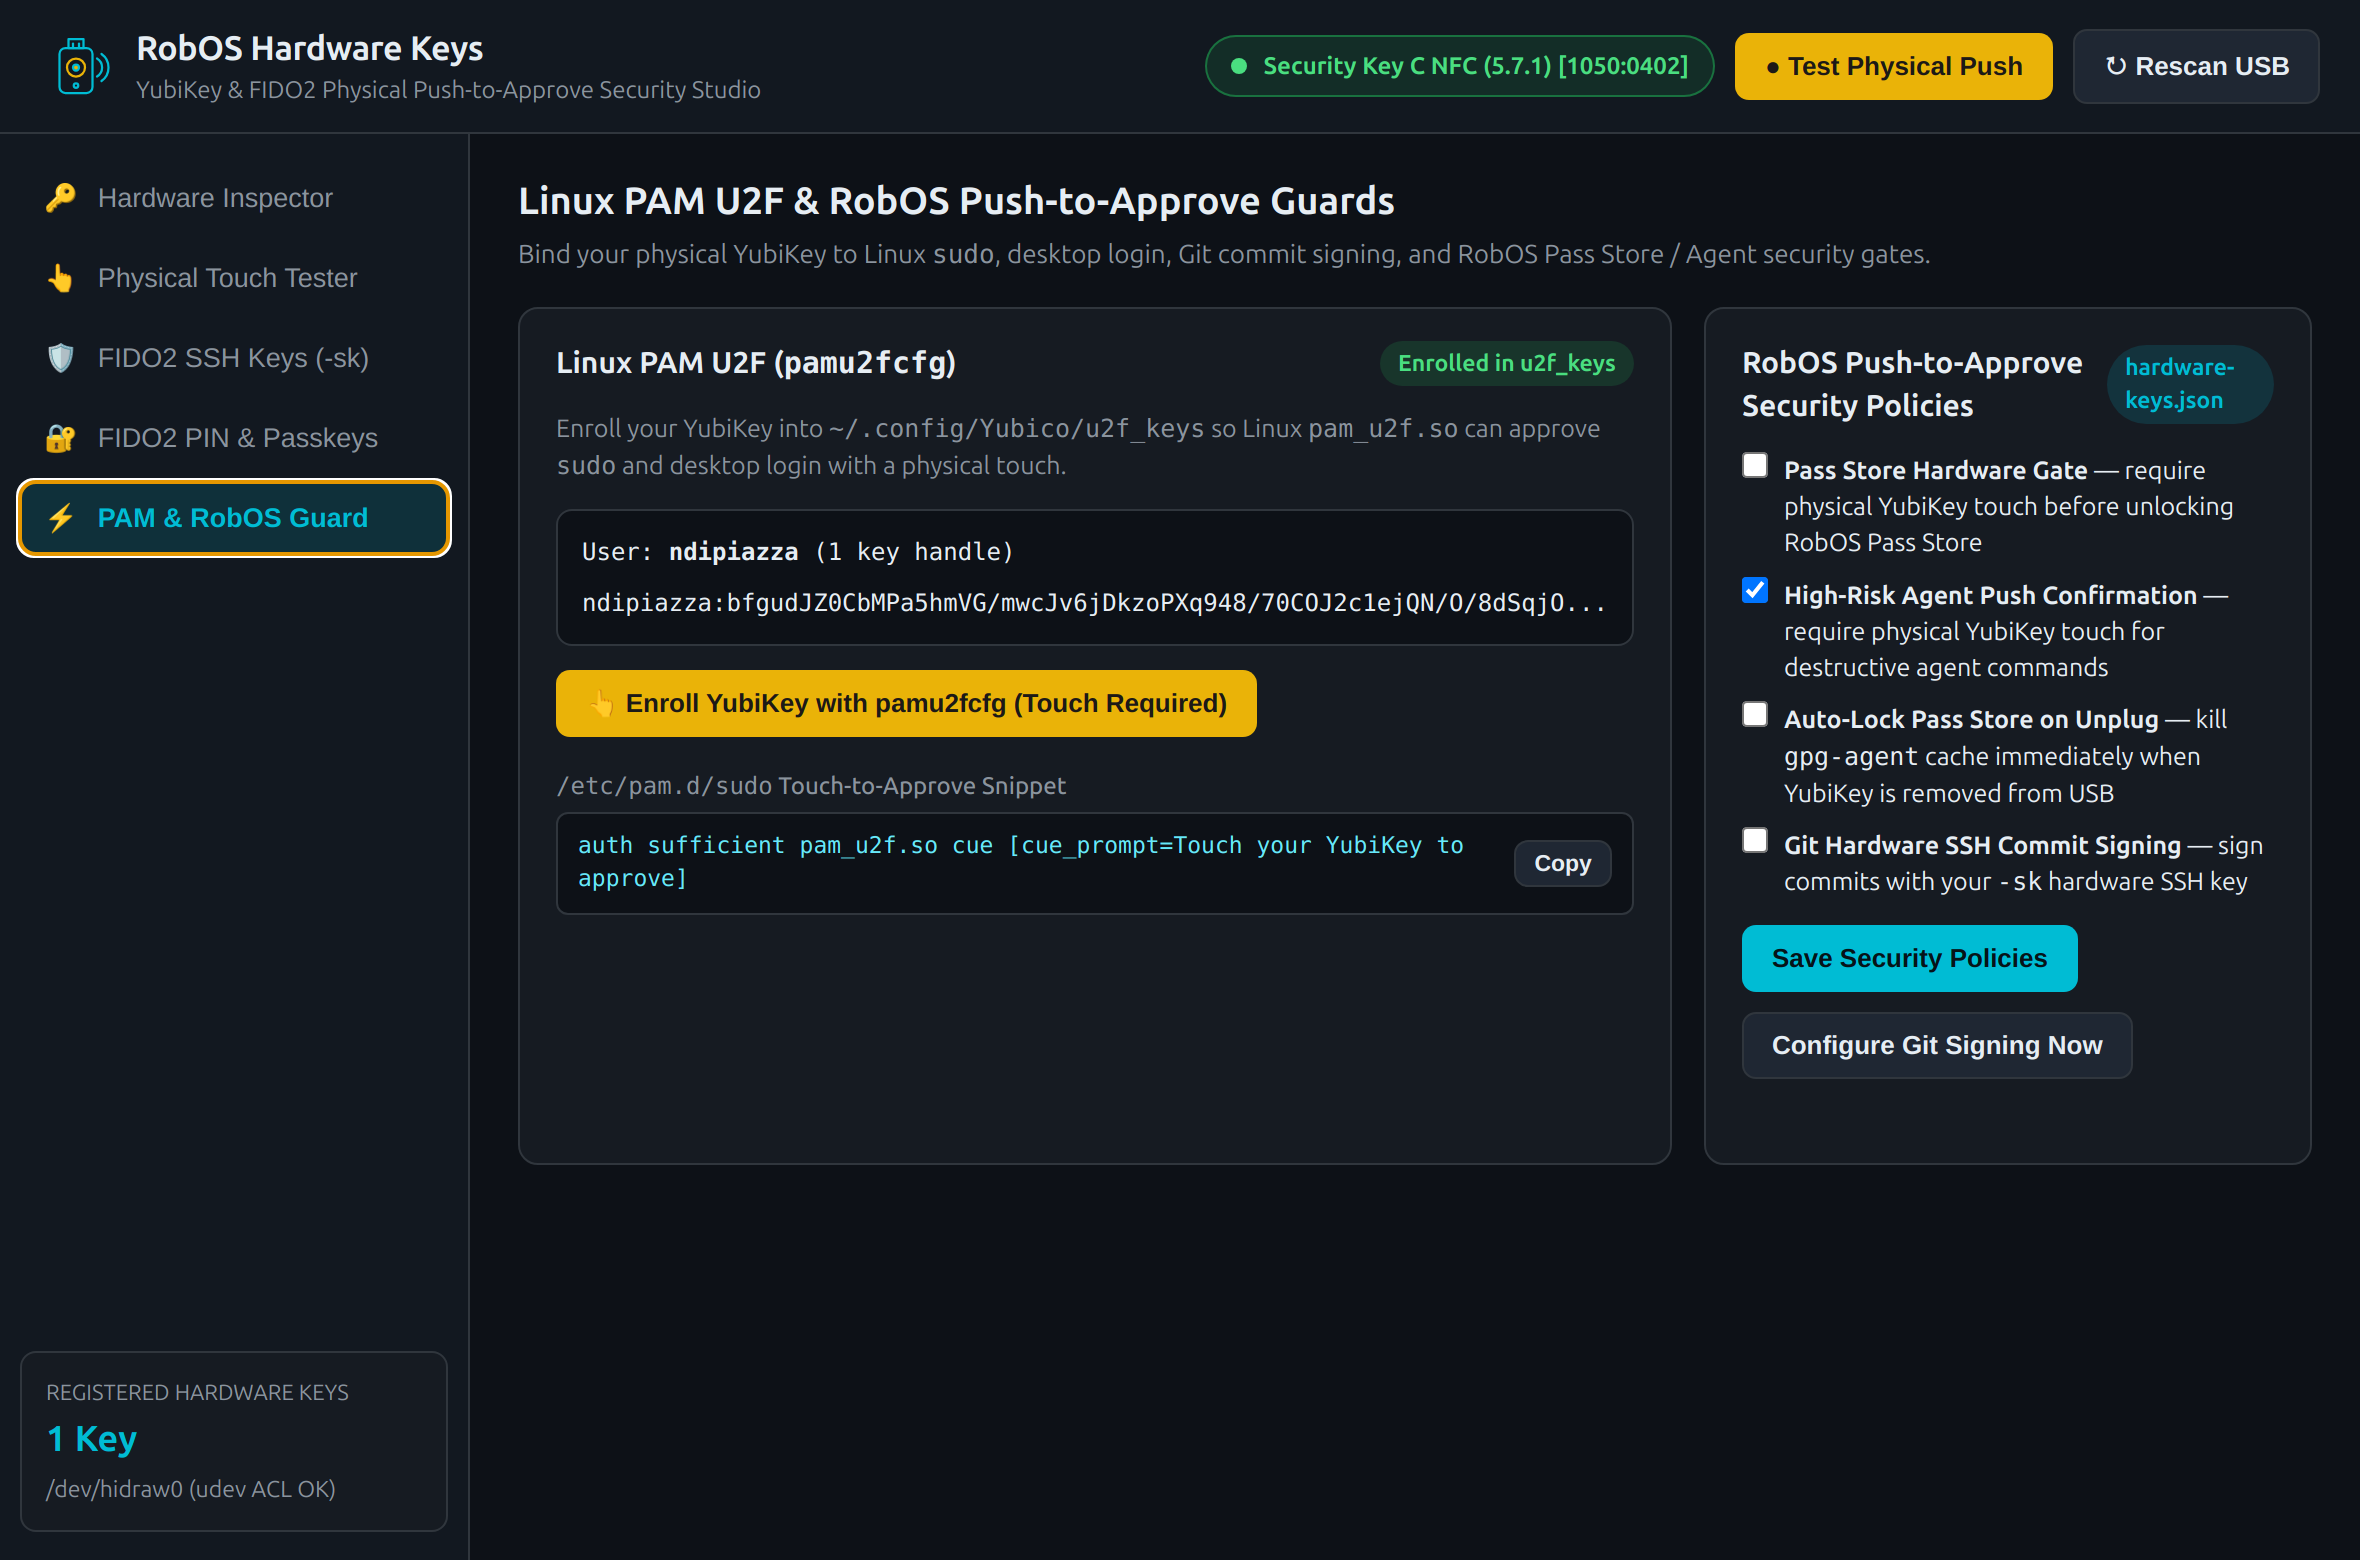
| FIDO2 PIN & Resident Passkeys | Linux PAM U2F & RobOS Guards |
|---|---|
 |  |
3. Capabilities & Workflows
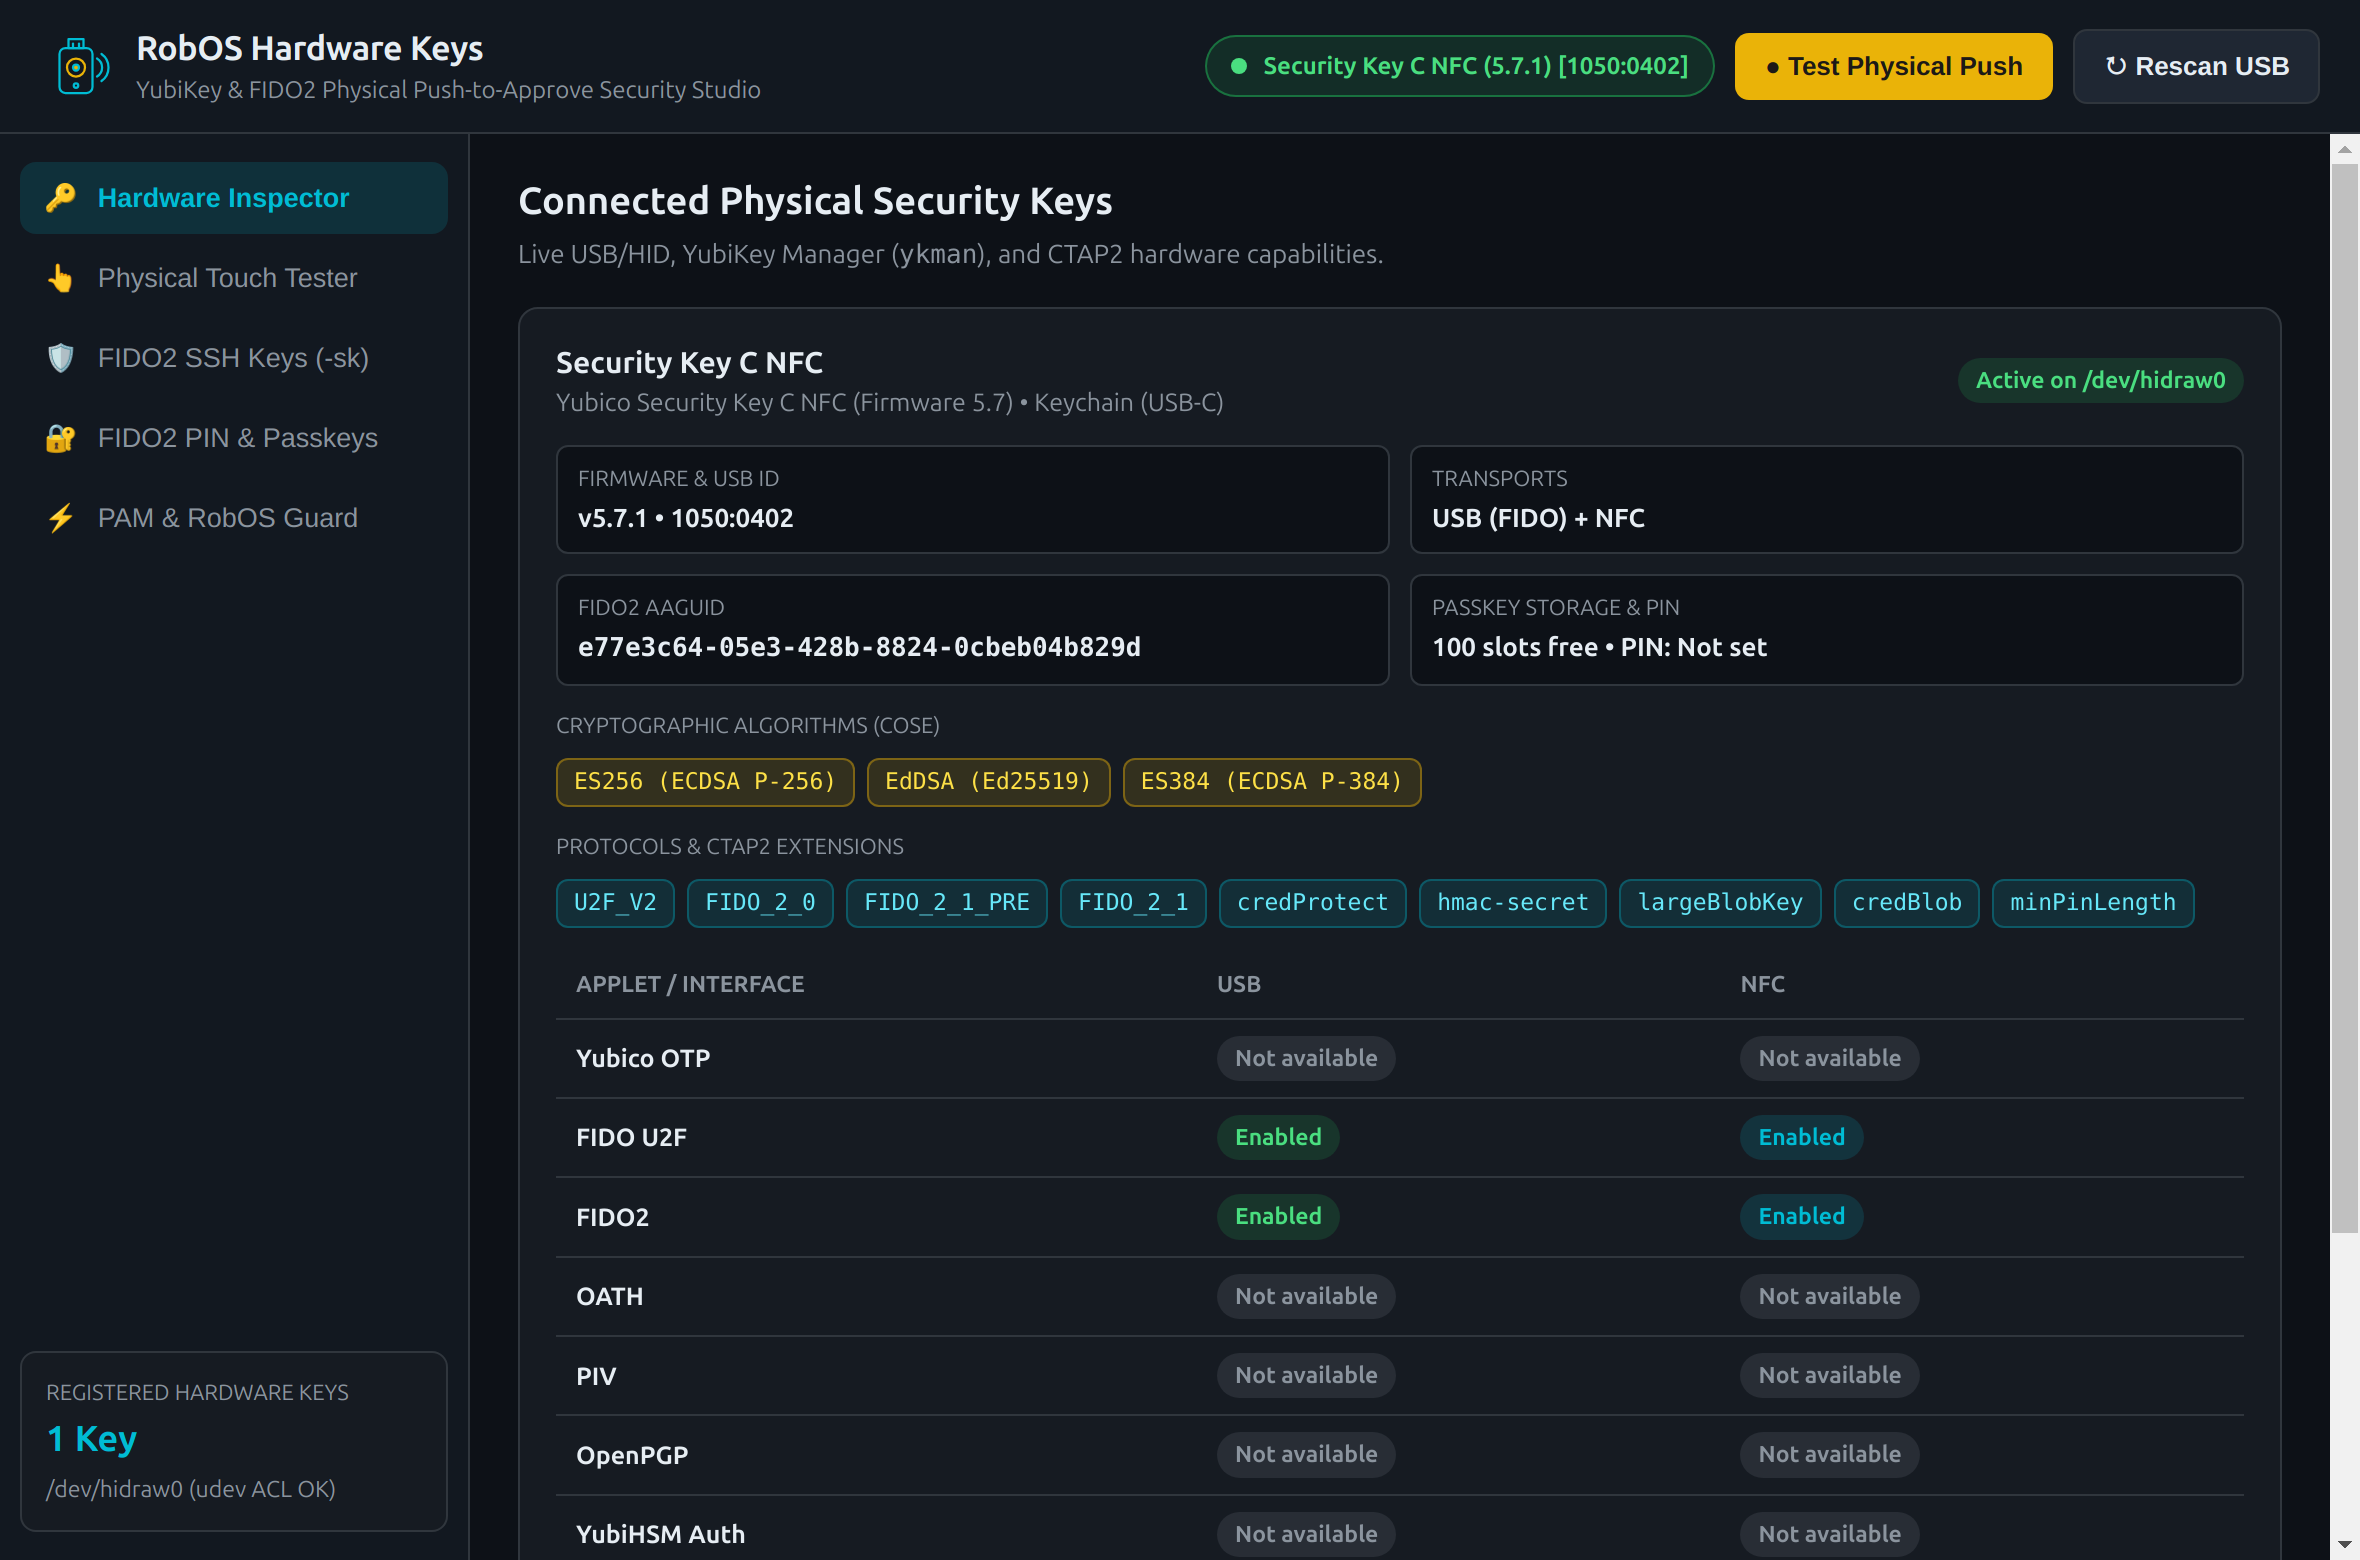
- Hardware Inspector: Queries
/sys/class/hidraw/hidraw*/device/uevent,ykman info,ykman fido info, andCtap2.get_info()to report firmware version, USB/NFC applet state, FIDO2 AAGUID, supported COSE algorithms (EdDSA / Ed25519,ES256 / P-256,ES384 / P-384), CTAP2 extensions, and Linux udev read/write permissions. - Physical Touch Verifier: Issues a live cryptographic challenge to the key, blinks the LED, measures physical touch latency in milliseconds, and displays the resulting hardware signature and authenticator flags (
UP=1,UV). - Hardware-Backed OpenSSH Keys (
ed25519-sk&ecdsa-sk): Generates FIDO2 SSH keys whose private half never leaves the YubiKey, supportsverify-requiredand resident (-O resident) modes, testsssh-keygen -Y signsignatures, and uploads.pubkeys to GitHub. - FIDO2 PIN & Passkeys: Sets or rotates the FIDO2 PIN (
ykman fido access change-pin) and lists or deletes discoverable resident credentials (ykman fido credentials list). - Linux PAM U2F & RobOS Guards: Enrolls
~/.config/Yubico/u2f_keysviapamu2fcfgfor touch-to-approvesudoand desktop login, configures Git global SSH commit signing (gpg.format = ssh), and can automatically lockgpg-agentwhen the YubiKey is unplugged.